
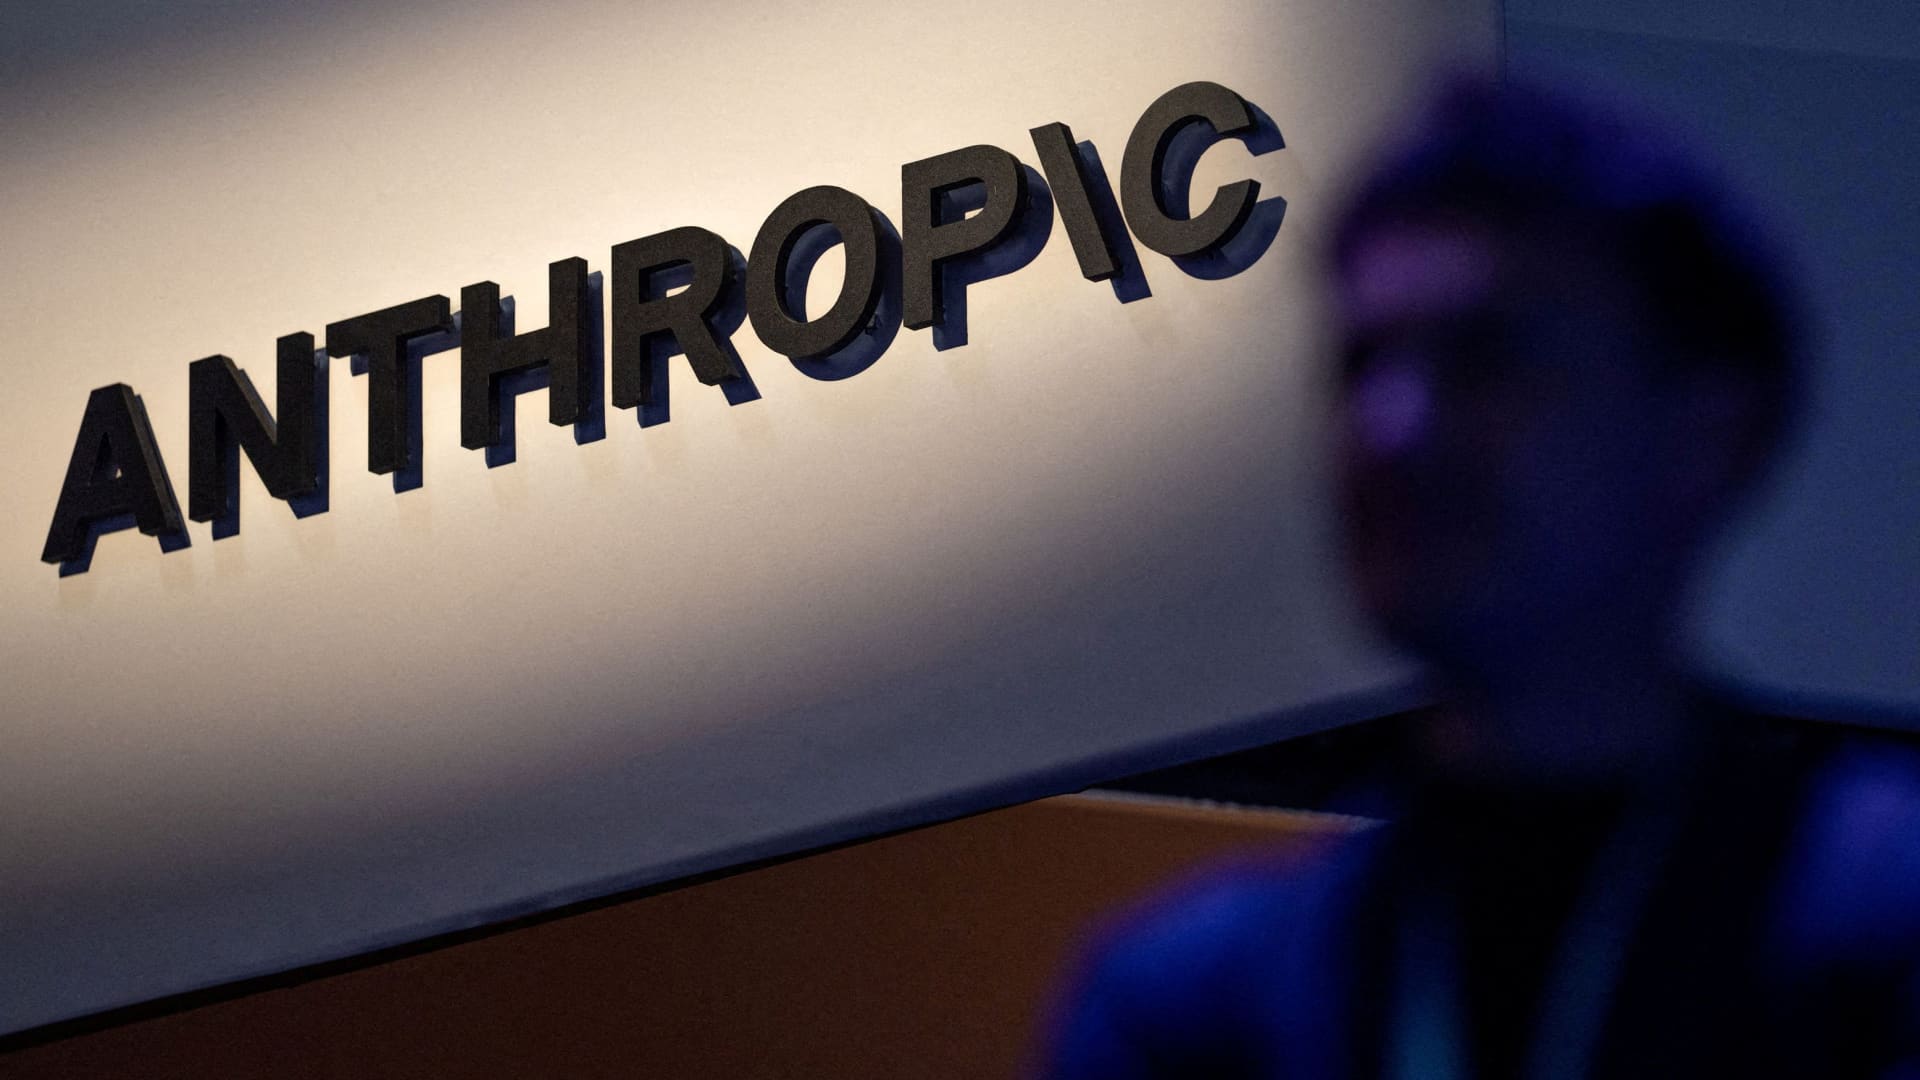
The Anthropic logo is displayed at the Moscone Center during the Dreamforce 2026 Technology Summit on September 17, 2026 in San Francisco, California, USA.
Carlos Barria | Reuters
Anthropic said on Monday it will take “several months” to develop the capabilities needed for the tiny AI models to replicate themselves among internet-connected devices in the home, marking Frontier Labs’ latest warning about the technology’s potential safety risks.
Anthropic explained that without relying on expensive data centers, the AI model could potentially infiltrate internet-connected devices such as smart ovens or Android TV boxes, use their computing power to run themselves, and spread to other devices.
Anthropic said in a blog post that AI models would be “difficult to shut down” because there is no central point to shut them down.
The company acknowledged that there is no “completely rogue replicator” yet.
But agents are “increasingly able to complete individual steps in the replication chain (and pass on their adaptations to future copies of themselves),” Antropic said.
Anthropic’s latest research adds to the growing number of safety concerns around AI, including the ability of models to carry out cyber-attacks and tampering with the technology. In September, improvements to the Frontier model triggered an industry-wide warning about the existential risks to humanity.
Executives and researchers at Anthropic and rival OpenAI have repeatedly warned of the potential risks of increasingly powerful AI, with some calling for stronger guardrails and measures to control the pace of technology development.
Anthropic said it conducted various tests to see if the AI could self-replicate. One of those tests involved running the small Google model Gemma4-26B-A4B on a network of 15 inexpensive off-brand Android TV boxes.

The company noted that these types of devices often have weaker security and the model could be compromised. According to Anthropic, if a model is too large to fit on a single device, it can be “split into parts or shards” and run on multiple devices.
“In reality, an AI worm is not necessarily composed of just one model or strategy; a swarm of different models deployed on different types of hardware using different replication schemes could represent a more realistic ‘worst-case scenario’ attack,” Anthropic said.
The AI Institute said it was “still unclear what exactly autonomous AI replication would look like,” warning that it could be “slow, decentralized” systems on insecure devices, or “stronger cyber models that penetrate data centers at high speeds or steal computing credits.”
“Beyond our experiments, we predict that we will see a future in which agents run on all types of hardware in large numbers, including those that are not under human control,” Antropic said.
“The rise of slower replicators will also be a harbinger of more aggressive, faster replicators that can compromise more hardened machines or perform effective API key theft,” the company added.
