
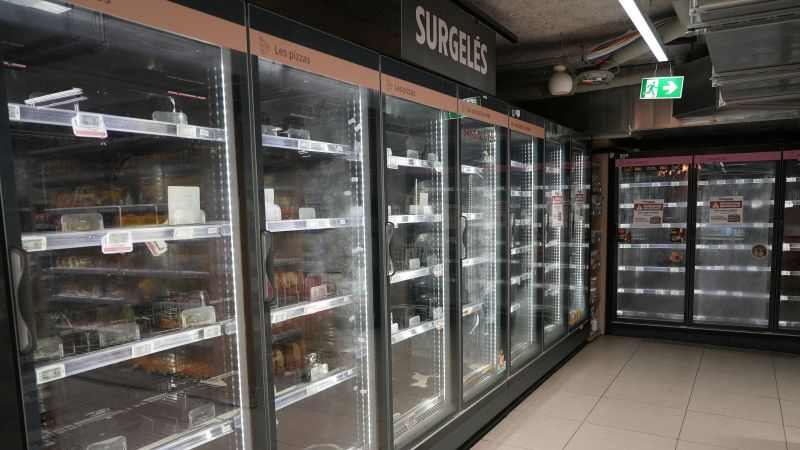
Earlier this week, supermarket workers were faced with water accumulating under the freezers and spoiling produce after hackers took over the refrigerators of hundreds of grocery stores across France.
According to CNN affiliate BFMTV, approximately 700 food retailers were affected by the nationwide cyberattack. In the cyberattack, hackers remotely connected to refrigeration equipment and turned on the defrost cycle, resulting in the loss of large quantities of fresh and frozen goods.
French authorities on Tuesday launched an investigation into what the country’s economy minister, Laurent Lescure, called a “wake-up call for everyone” in a speech to parliamentarians.
Here’s what you need to know:
No one has yet claimed responsibility for the cyber attack. Ken Munro, a UK-based cybersecurity analyst, told CNN that the fact that the hackers did not publicly demand a ransom (as is often the case) meant their main goal was to play a “prank” and “spook the public.”
Felix Aime, chief threat researcher at French cybersecurity firm Sequoia, said the hacker’s motives were “unknown at this stage.” “As far as we know, there has been no official claim of responsibility,” added Aime, who previously worked for France’s national cyber agency ANSSI, which is currently in charge of the investigation.
Emme said he could not rule out the possibility that a lone hacker or hacktivist group carried out the attack. “Operations aimed at destabilizing specific economic activities or infrastructure may also be considered,” he told CNN.
Additionally, Emme added that the culprits do not appear to have used any malicious code on the refrigerator controllers, which could complicate efforts to track down the perpetrators of the cyberattack.

In a statement to CNN on Tuesday, the Paris public prosecutor’s office announced that it had brought the incident under national jurisdiction as a “large-scale cyberattack that affected the connected refrigerators of several major food retailers across France.”
The investigation will “identify the victims and determine the relationship between the damage, such as food spoilage and fire, and the damage reported by the victims,” the statement added.
Grocery store refrigerator and freezer aisles are operated by controllers that can be accessed online, allowing maintenance companies to adjust temperatures remotely. In France, hackers broke into controllers operated by at least three companies, including Danish company Danfoss, US-based company Copeland and Dixel, according to a statement from ANSSI to CNN.
Immediately after the cyberattack, Danfoss acknowledged that many of the affected units were “not receiving software or security updates” or were “running outdated software.” The company urged customers to “keep updating their supported systems with the latest firmware.”
Copeland, which owns Dixell, identified a “vulnerability” in “a generation of controllers that is no longer in production and has reached the end of its useful life.” “We are currently working with affected customers to mitigate risk,” the company told CNN in a statement.
CNN has reached out to Danfoss for comment.

Munro, a partner at British cybersecurity organization Pen Test Partners, said the Danish company, a refrigerator installer, may have mistakenly put the controller on the public internet “for everyone to see.”
Prior to the cyberattack, more than 1,700 instances of the affected Danfoss software were exposed on the French internet, creating a wide potential target pool for hackers, Aime said.
Earlier this year, cybersecurity firm Claroty cited vulnerabilities in the Danfoss AK-SM 800A, the controller at the center of the attack, in a report published in early August, citing mechanisms that “could be exploited” to “bypass normal authentication.” Emme added that the vulnerability could allow an attacker to remotely change the temperature settings of a refrigerator running the affected software.
According to security analysis firm UK Cyber Defense, the attackers used the device’s built-in defrost function to defrost the refrigerator overnight by removing restrictions that would normally prevent it from overheating. Temperatures at the shelves reached a peak of 50 degrees Celsius (122 degrees Fahrenheit) for about six hours Monday night, with some fires breaking out.
“Finding a way to manage the refrigerators was not difficult,” Munro said, adding that unit management at these retailers “is likely outsourced to third parties with little or no regard for maintaining the security of the refrigerators.”

A major French supermarket group was also hit by the attack, with retail executives warning that losses could run into the millions of dollars.
Some 80 supermarkets under French brand Carrefour were affected, as were 5% of Monoprix’s 490 stores. Retail group Les Mousquetaires reported that refrigerators in 150 stores were targeted. About 80 Cooperative U stores were also affected, said Dominique Schelcher, the company’s CEO.
And this problem does not seem to be contained within France. Emme told Reuters that Spain, Portugal, Poland, Germany and Belgium were also affected by the attack.
For consumers, Munro says there’s not much to worry about. However, he cautioned that the refrigerator management systems involved must be “secured from the public internet” with verified security.
“My business didn’t need to be able to access the refrigerator controller on the public internet,” he said. “My recommendation is for company boards to ask probing questions of their suppliers: Who outsourced the management of these refrigerators and who was contractually monitoring their safety? It doesn’t take much for a company to have one blind spot and a lot of food goes to waste.”
The attack prompted a wave of criticism from European officials, just weeks after French President Emmanuel Macron told lawmakers to draw up a new protection plan against the growing threat of cyberattacks at home and abroad.
After meeting party leaders in Paris in September, Macron spoke to reporters about the “Russian hybrid threat facing Europe and France,” adding that the risk had “intensified” in recent weeks, according to Reuters.
EU Agriculture and Food Commissioner Krisof Hansen warned that food security requires increased attention at all levels. “Weaponization of food has become a reality,” he wrote on X on Monday.
France’s Economy Minister Les Couré allayed concerns about the risk of food shortages in the country, but called on providers to strengthen cybersecurity measures.
“When we discovered this cyber attack, we were concerned about the ability of our distribution chain to adequately deliver food to all our citizens,” he said on Tuesday. “This is a wake-up call to everyone.”
CNN’s Sean Ringers contributed reporting.
