
European countries are struggling to respond to a spate of unprecedented explosion threats across Europe, with it still unclear who is behind the incidents.
The threats, which are said to have been primarily sent by email and have all been proven false so far, have affected multiple media outlets, more than 50 flights, thousands of schools and at least one cruise ship across the continent, posing an increasingly urgent security challenge for European authorities.
Analysts say the hoax exposes the vulnerability of Europe’s public infrastructure to anonymous and hard-to-trace messages and highlights the need for a more coordinated response from European countries.
Bomb threats targeting flights in Europe were taken seriously by authorities, and strong measures were taken, depending on the country. Some authorities diverted flights to other airports, while others, including Hungary and France, scrambled fighter jets to escort the affected airliners.
Some in Europe are calling for bloc-wide security frameworks to replace fragmented national responses. József Varady, chief executive of Hungarian low-cost carrier Wizz Air, spoke on Thursday of the need for more harmonized security procedures and hinted at the possibility of establishing a central authority to control such disinformation.
He said he had recently met with European Commission officials to encourage a coordinated response. “But this is a very thorny issue because of the concept of sovereign states, and no country wants to compromise on this issue,” Varady said in a post-earnings conference call Thursday.
Threats targeting airlines operating across multiple countries can involve multiple law enforcement agencies, and increased intelligence sharing between countries can be key to identifying patterns and determining the origin and validity of threats.
Grégoire Rouss, director of the Europe, Russia and Eurasia program at London-based think tank Chatham House, said the initial security response was strong but coordination among European countries remained weak.

He told CNN that because the threat is a relatively new phenomenon, each country is currently responding with “its own toolbox and standards.”
He believes the first step towards improvement is establishing a European-wide threat assessment standard. “For example, emergency measures should depend on supporting information and the circumstances of each incident at continental level.”
He also believes that whoever is behind the attack is taking advantage of differences in domestic procedures. “Europol, national police and possibly local police and aviation authorities all need to compare the technical evidence.
“So, in a sense, there’s a disorganized response, and within that disorganized response there are sub-levels. So there’s a longer reaction time and therefore more room for anxiety to increase.”
The threat also reveals that while it is low cost to launch such a hoax, it is much more expensive to counter it. A single email can force a massive security deployment, divert a plane, or prompt the evacuation of a public building. Such methods place a heavy burden on public resources, disrupt daily life, and cause public anxiety.
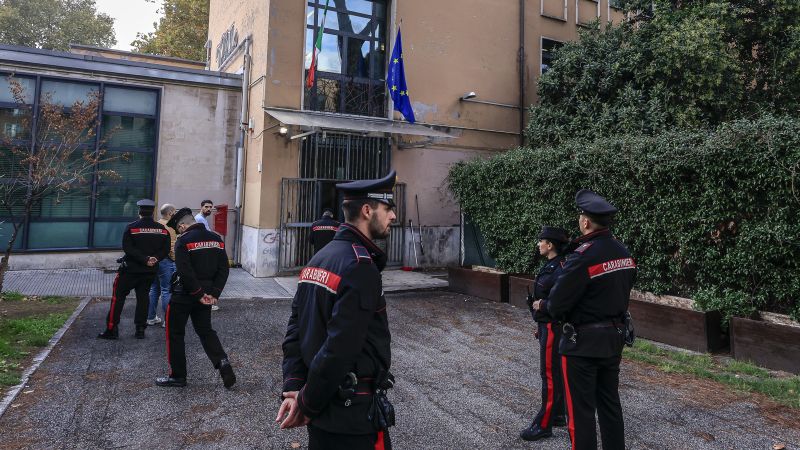
One response is to try to continue life as normal. When thousands of schools in Italy received threats this week, Prime Minister Giorgia Meloni sent an overriding message to worried parents: to remain calm and minimize disruption.
Bomb threats were emailed to about 6,300 Italian schools on Wednesday and to about 3,778 Italian schools on Thursday. Hundreds of schools were evacuated, but many also chose to remain open. Meloni proposed new evacuation procedures in response to the threats, stipulating that schools should not be evacuated based solely on mass emails without concrete evidence.

Schools in Scotland, Northern Ireland and the Republic of Ireland also received threatening emails on Wednesday. Police warned that these were likely hoaxes and that educational facilities had not been evacuated.
Meanwhile, some UK airports have decided to remain open despite threats.
“As far as the UK is concerned, we’ve seen Heathrow and Birmingham airports receive threats and still manage to stay open because they’ve been rated as unreliable. So I think this is something that other countries across Europe could do, rather than saying, ‘Okay, we’ve got a mild alert, so we’re going to close everything,'” Ruth said.
He added: “This is more important than you might think, because the moment you evacuate, your anxiety level increases.”
The digital nature of the alerts (the majority of them were sent via email) makes it difficult for investigators to trace their origin. Some of them have been endorsed by certain groups, such as Russia’s ultranationalist group Mare State, but authorities suspect these may be false attributions.
Cybersecurity companies Proofpoint and Abnormal Security found that the majority of threats were sent from legitimate webmail accounts that had been hijacked. Such practices can make it difficult for law enforcement to track down those responsible and leave authorities in a reactive position.
There is strong suspicion that these incidents may be part of a broader campaign of so-called hybrid warfare, in which adversaries seek to undermine public trust and destabilize states without resorting to conventional military force.
European officials have increasingly warned of the threat posed by such tactics, and Russia is frequently accused of using cyberattacks, sabotage and disinformation to undermine the West. The Russian government has repeatedly denied involvement in these activities.
But French President Emmanuel Macron on Thursday warned against jumping to conclusions about the wave of bomb threats, saying there was still no evidence that foreign powers were responsible for the wave.

“As I speak, there are not enough elements to establish attribution,” Macron told reporters at a European summit in Dublin.
Roos cautioned against automatically blaming Moscow without concrete evidence, saying this could embolden other potential actors. “If we immediately attribute every threat to Moscow without investigating it, we run the risk of empowering, for lack of a better word, the many perpetrators, both state and non-state actors,” he said.
It also remains unclear whether threats across schools, airlines, broadcasters, and other institutions are related or stem from a single individual, group, or state-sponsored operation.
The challenge now is to strike a balance between taking all potential threats seriously and ensuring that anonymous emails don’t repeatedly take down critical services.
As incidents continue across borders, pressure is likely to increase on European governments to establish a more coordinated approach, one that can differentiate between credible security threats and attempts to exploit the very precautions meant to protect their populations.
