

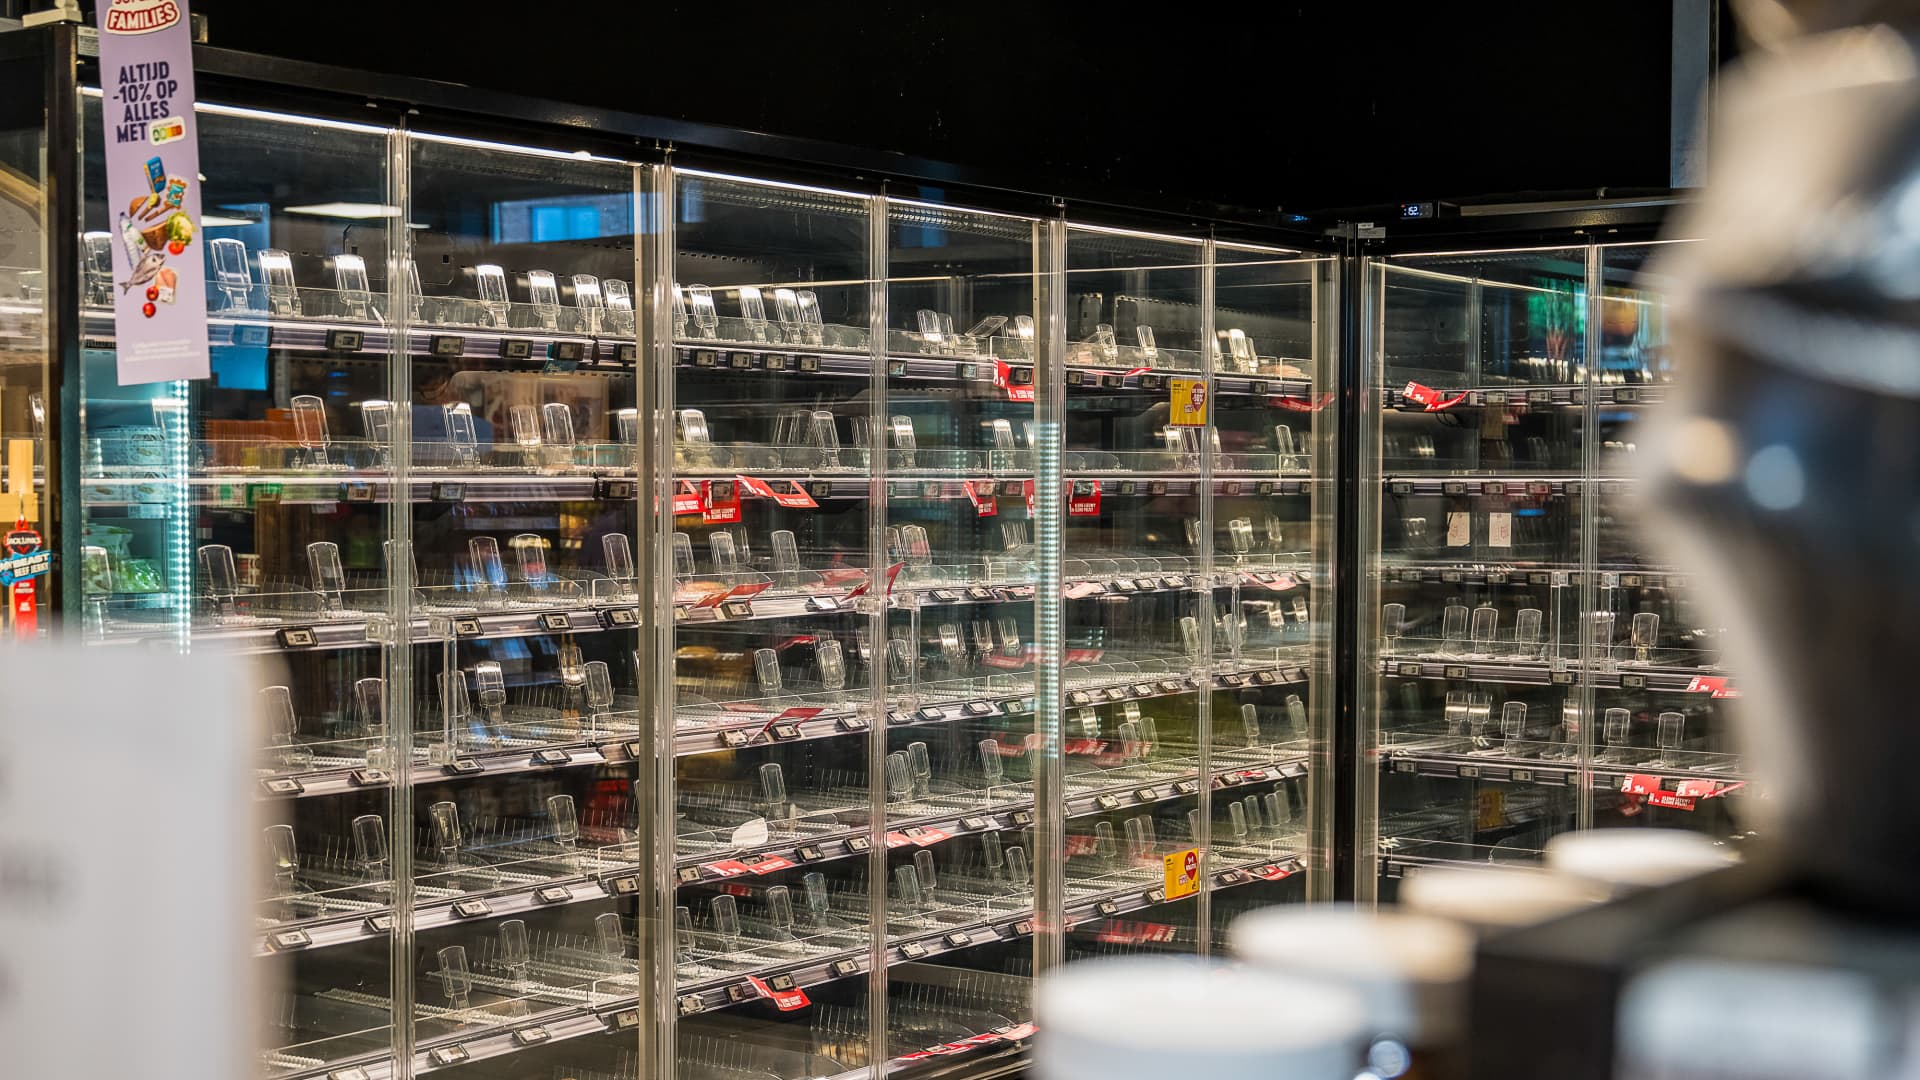
Refrigerated shelves are empty after refrigeration was shut down at the Proxy Delhaize store in Mareisen, Overijse, Belgium, on Monday, November 2, 2026.
Bloomberg | Bloomberg | Getty Images
European supermarkets have become the center of a new cyberattack, with hackers remotely heating refrigerators and spoiling food.
The attack reportedly caused refrigerator and freezer temperatures to rise sharply, reaching temperatures of up to 50°C (122°F) in at least one store, while other retailers were forced to throw away food. This is causing concern throughout the retail industry.
Which countries and retailers were affected?
Dutch supermarket group Ahold Delhaize Dozens of stores in Delhaize were reportedly affected in Belgium and Luxembourg.
The Dutch supermarket giant told CNBC that dozens of its stores suffered failures with refrigeration systems on Monday, resulting in food having to be thrown away. The company said the situation has since returned to normal and its stores are fully operational.
meanwhile, collite group According to Reuters, the company announced that five Spar stores in Belgium were targeted. french supermarket carrefour He told the BBC that 15 of the Belgium-based company’s stores were also attacked. France’s Intermarché also announced that 15 of its 153 stores in Belgium were affected.
“In most cases, we were able to quickly stop the attack due to the security measures in place,” an Intermarche spokesperson told CNBC. “However, some stores experienced inventory losses, although not comparable to the attacks in mid-October.
“The information available to us at this stage indicates that the majority of the attacks affected other companies in the sector, in particular Carrefour and Delhaize,” they added.

IKEA told CNBC that a cyber incident affected refrigerators and freezers at its Mons store in Belgium between Sunday and Monday.
While the store is still open to customers, the company is inspecting the affected equipment and products and inspecting the overall installation of its other stores in Belgium.
“This incident has had a limited impact on our restaurant and Swedish Food Market offerings,” an IKEA spokesperson said in an email. “We are continuing to investigate to determine exactly what happened.”
ICA, Sweden’s largest grocery retailer, also confirmed that it had been informed of the incident at a “limited number of stores” on its network outside of ICA’s central system. “This incident impacted the store’s refrigeration and freezing systems. ICA is currently assisting affected stores with their response,” the company said in an email.
Also reporting problems with their refrigeration systems were Finnish supermarket Kesko, Irish grocery chain Supervalu and Estonian grocery store One Cellbar.
Carrefour did not immediately respond to CNBC’s request for comment.
How is Monday’s incident related to October’s cyberattack?
In October, hundreds of supermarkets in France were targeted by a cyber attack that caused fires, overheated refrigerators and spoiled food.
Inter Marche owner Les Mousquetaire told CNBC at the time that he expected damages to be in the millions of euros.
“Food security requires increased attention at all levels, as the weaponization of food is a reality,” European Commissioner for Agriculture and Food Christoph Hansen told the X program in October.
In late August, freezers at kiosks at six U.S. military bases also malfunctioned.
The Pentagon is now treating these as suspected hacks and coordinating with French authorities, four people familiar with the matter told Reuters in October.
In one case, the temperature in the refrigerator rose overnight, causing chunks of food to melt and wilt by morning.
Rafe Pilling, senior director of threat intelligence at the Sophos Counter Threats Unit, told CNBC that while there is no evidence that AI was involved in these attacks, criminals elsewhere are using AI to accelerate the scale and efficiency of their attacks.
Why is this happening?
Although this attack is not yet attributed to any group or malicious actor and an investigation is ongoing, it does raise concerns about vulnerabilities in critical infrastructure.
According to researchers’ information published in August, Visente AB’s strategic cybersecurity advisor Fredrik Blix said the hack itself was not sophisticated because the refrigerator’s control unit was “installed directly on the public internet” and included a support login feature that allowed same-day password retrieval.
“The vendor applied the patch in August,” Blix said in a LinkedIn post. “Thousands of units are unable to get updates, and the oldest models cannot be updated at all.”
He added that France was also hit by the same attack three weeks ago, and France’s CERT-FR had instructed European carriers to remove devices from the internet. “The question I asked the suppliers and service companies that installed and remotely managed this kit was: What exactly did you do in those three weeks?”
Blix noted that the silence behind the attack is the most “interesting clue” to eliminate the ransomware perpetrator, leaving two options. Blix said either someone carried out the attack simply because they could, or someone wanted to cause “anxiety in countries supporting Ukraine without leaving any fingerprints.”
